David Thiery, CISSP · Cybersecurity executive

Cybersecurity.
Business resilience.
Trust.

I'm David Thiery, CISSP, a Chief Information Security Officer and cybersecurity expert based in Michigan. I help healthcare and insurance organizations translate cyber risk into clear priorities, stronger security programs, and business resilience.

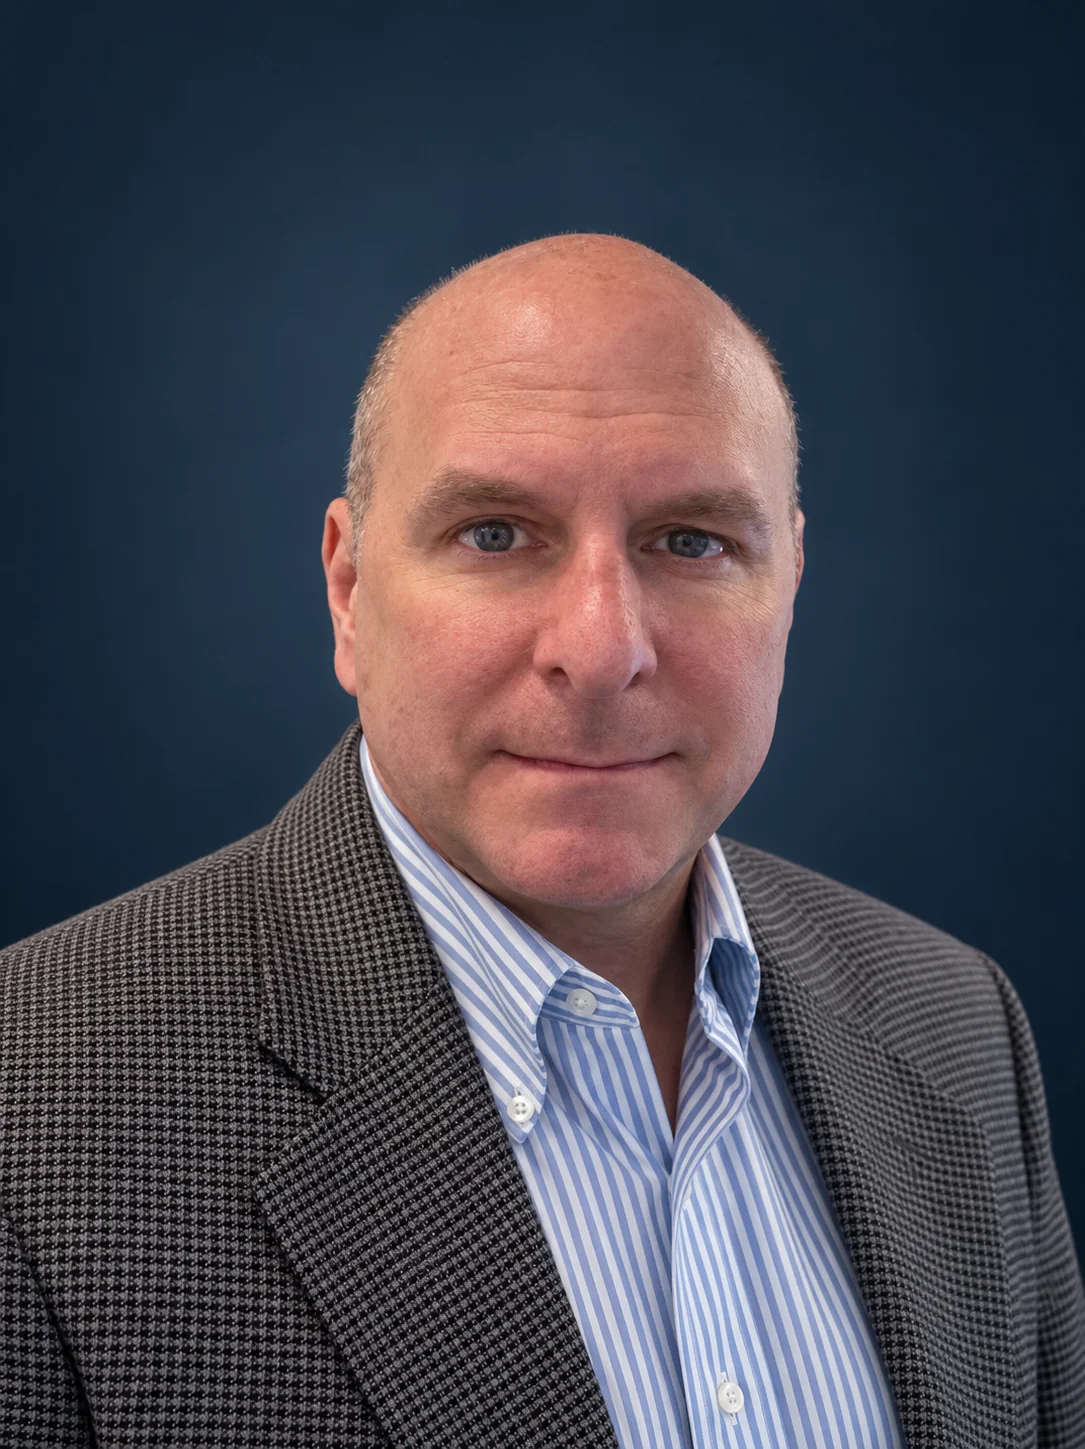
David Thiery, CISSP, Chief Information Security Officer and cybersecurity expert
DAVID THIERY CISSP
CHIEF INFORMATION SECURITY OFFICERHEALTHCARE & INSURANCEBOARDROOM PERSPECTIVE. OPERATIONAL DEPTH.
25+ years
Technology & security experience
1,500+
Employees supported by current security program
100+
Hospitals in national ERP rollout
The perspective I bring

Cybersecurity expertise.
Business leadership.

CYBERSECURITY EXPERTISE. ENTERPRISE CONTEXT.

I bring more than 25 years of technology and security experience to enterprise cybersecurity, with a focus on healthcare, insurance, and benefits administration.

My work connects cybersecurity strategy, governance, risk and compliance (GRC), security operations, and cloud security. I advise boards and executive teams on cyber risk while working with technical leaders to protect sensitive health information and sustain critical business operations.

My leadership approach is transparent and empowering: give people clear ownership, remove obstacles, and invest in their development. I combine that approach with experience leading governance, HITRUST initiatives, and technology integration across 180 ambulatory locations.

Areas of expertise

Enterprise cybersecurity
from strategy to execution.

Security leadership that connects executive decisions with the work required to protect the enterprise.

Cybersecurity strategy & governance

Translate enterprise cyber risk into security roadmaps, board reporting, investment priorities, and accountable remediation. Experience includes NIST Cybersecurity Framework (CSF), NIST 800-53, third-party risk management, and M&A cybersecurity due diligence.

Executive advisory · NIST · Enterprise risk

Security operations & response

Lead security operations center (SOC) oversight, managed detection and response (MDR), incident response, and threat-informed vulnerability management. Connect SIEM and endpoint detection and response (EDR) capabilities with penetration testing and remediation priorities.

SOC & MDR · SIEM · Incident response

Compliance & assurance

Lead audit readiness, risk remediation, and security governance for regulated healthcare and insurance environments. Experience spans SOC 2 Type 2 audits, HITRUST implementation, HIPAA and HITECH requirements, and security awareness programs.

SOC 2 · HITRUST · HIPAA / HITECH

Resilience & secure transformation

Strengthen business continuity and disaster recovery while supporting secure technology change. Experience includes Azure, AWS, Microsoft 365, identity and access management (IAM), multifactor authentication (MFA), privileged access management (PAM), and security by design.

BC / DR · Cloud security · M&A integration
Selected career impact

Experience measured
in real responsibilities.

A selection of the programs and transformations I’ve led across security and enterprise technology.

Harbour Benefit Holdings / Zenith American Solutions

Enterprise security leadership at national scale.

Lead security and privacy teams supporting a 1,500+ employee organization across 40+ locations. Led efforts achieving SOC 2 Type 2 audits with zero exceptions for two consecutive years, alongside board reporting and enterprise risk governance.

Triarq / BCBS of Michigan

Building governance into healthcare operations.

Led the GRC committee and risk remediation work, directed HITRUST implementation, and managed security awareness and controls across healthcare applications.

Demant / ANA / Birdsong

Designing for recovery before disruption.

Developed a business continuity and disaster recovery plan with a one-hour recovery point objective and a 30-minute recovery time objective, alongside hybrid cloud infrastructure and security controls.

Ascension / St. John Providence

Leading transformation across complex environments.

Managed a national Oracle / PeopleSoft ERP implementation across more than 100 hospitals and led technology integration across 180 ambulatory locations.

Leadership experience

Cybersecurity & technology
leadership experience.

Explore the roles behind the perspective.
Select a role to see more.

2024 — PresentChief Information Security OfficerHarbour Benefit Holdings / Zenith American Solutions

Direct enterprise cybersecurity strategy, privacy, governance, and security operations for a nationwide healthcare and benefits administration organization supporting more than 1,500 employees across 40+ locations. Advise the board, executive leadership, and private equity stakeholders on cyber risk, audit readiness, and security investment priorities.

Oversee internal SOC and MDR services, incident response, vulnerability management, penetration testing, and cloud security governance. Lead security controls across identity, endpoints, applications, and third-party services. Supported two consecutive SOC 2 Type 2 audits with zero exceptions and guide cybersecurity due diligence and post-acquisition integration.

2021 — 2024Vice President, Value & ComplianceTriarq / BCBS of Michigan

Led governance, risk and compliance (GRC), technology risk remediation, and internal and external audit coordination for a healthcare technology and value-based care organization. Directed HITRUST implementation and HIPAA remediation, translating regulatory and security requirements into operational controls.

Strengthened data protection, identity and access management, multifactor authentication, endpoint security, and security awareness. Directed offshore software delivery for provider and consumer-facing applications, incorporating HIPAA, HITRUST, NIST, and OWASP guidance into development and release planning.

2015 — 2021Vice President IT & SecurityDemant / ANA / Birdsong

Built and led enterprise technology and information security capabilities for a healthcare organization from startup through acquisition. As HIPAA Security Officer, directed security governance, infrastructure, application development, DevOps, privacy, and support operations.

Implemented hybrid cloud architecture, security monitoring, identity controls, privileged access management, and application modernization. Developed business continuity and disaster recovery plans with a one-hour recovery point objective (RPO) and a 30-minute recovery time objective (RTO), connecting recovery planning to operational requirements.

2009 — 2015National Program Manager & IS DirectorAscension / St. John Providence

Directed complex healthcare technology programs spanning a national Oracle/PeopleSoft enterprise resource planning (ERP) rollout across more than 100 hospitals and electronic medical record (EMR) and revenue cycle integration across 180 ambulatory locations.

Managed distributed technology resources and vendor partnerships across application development, infrastructure, data center consolidation, and enterprise data integration. Led shared services and disaster recovery initiatives supporting mission-critical clinical and business platforms.

1997 — 2009Information Technology DirectorNGS Coresource / Trustmark

Led a 45-person technology organization supporting insurance and third-party administration operations across application development, infrastructure, networking, telecommunications, electronic data interchange (EDI), and service delivery.

Directed claims platform development, high-availability infrastructure, enterprise firewall deployment, and secure software development controls. Combined technology modernization with operational improvement, including $2.4 million in print and mail savings over three years.

Professional foundation

CISSPCertified Information Systems Security Professional

BS in Management · Franklin UniversitySumma Cum Laude · 4.0 GPA

Former PMP certification · 2006–2016
Start a conversation

Let’s talk security,
resilience, and leadership.

Connect with me to discuss cybersecurity leadership, enterprise risk, and the challenges facing healthcare and insurance organizations.